Manage staff access
Assign roles and extra permissions or safely import and export access definitions. Effective permissions update only after validation and remain inspectable.
- Status
- Draft, not yet re-verified
- Who can do this
- Studio owners, Organization owners
- Required access
organization.owner- Where in PositiveForm
/settings/staff/:staffId/permissions
"Copy for AI" puts the full Markdown of this page on your clipboard. Paste it into ChatGPT, Claude, or any assistant and ask it to walk you through the steps.
Who this is for
This guide is for the organization owner deciding what one staff member can reach.
A person's access is the sum of two things: the roles you give them, and any direct grants for that person alone. Roles are the maintainable half; direct grants are the exception.
Access applies across the whole organization. Home and work locations do not narrow it. Someone with billing permissions has them at every location, whatever workspace opens for them by default.
Before you begin
- Build the roles first, in Settings › User roles; see Manage reusable roles. Assigning a role you already trust is safer than ticking permissions one at a time.
- Consider previewing the role before assigning it, so you see what it actually reaches; see Preview a role safely.
- Owners are not editable here. An owner holds every permission, and the page says so instead of offering switches that would not work.
Steps
- Click Settings in the left navigation, then click Staff, then click the person.
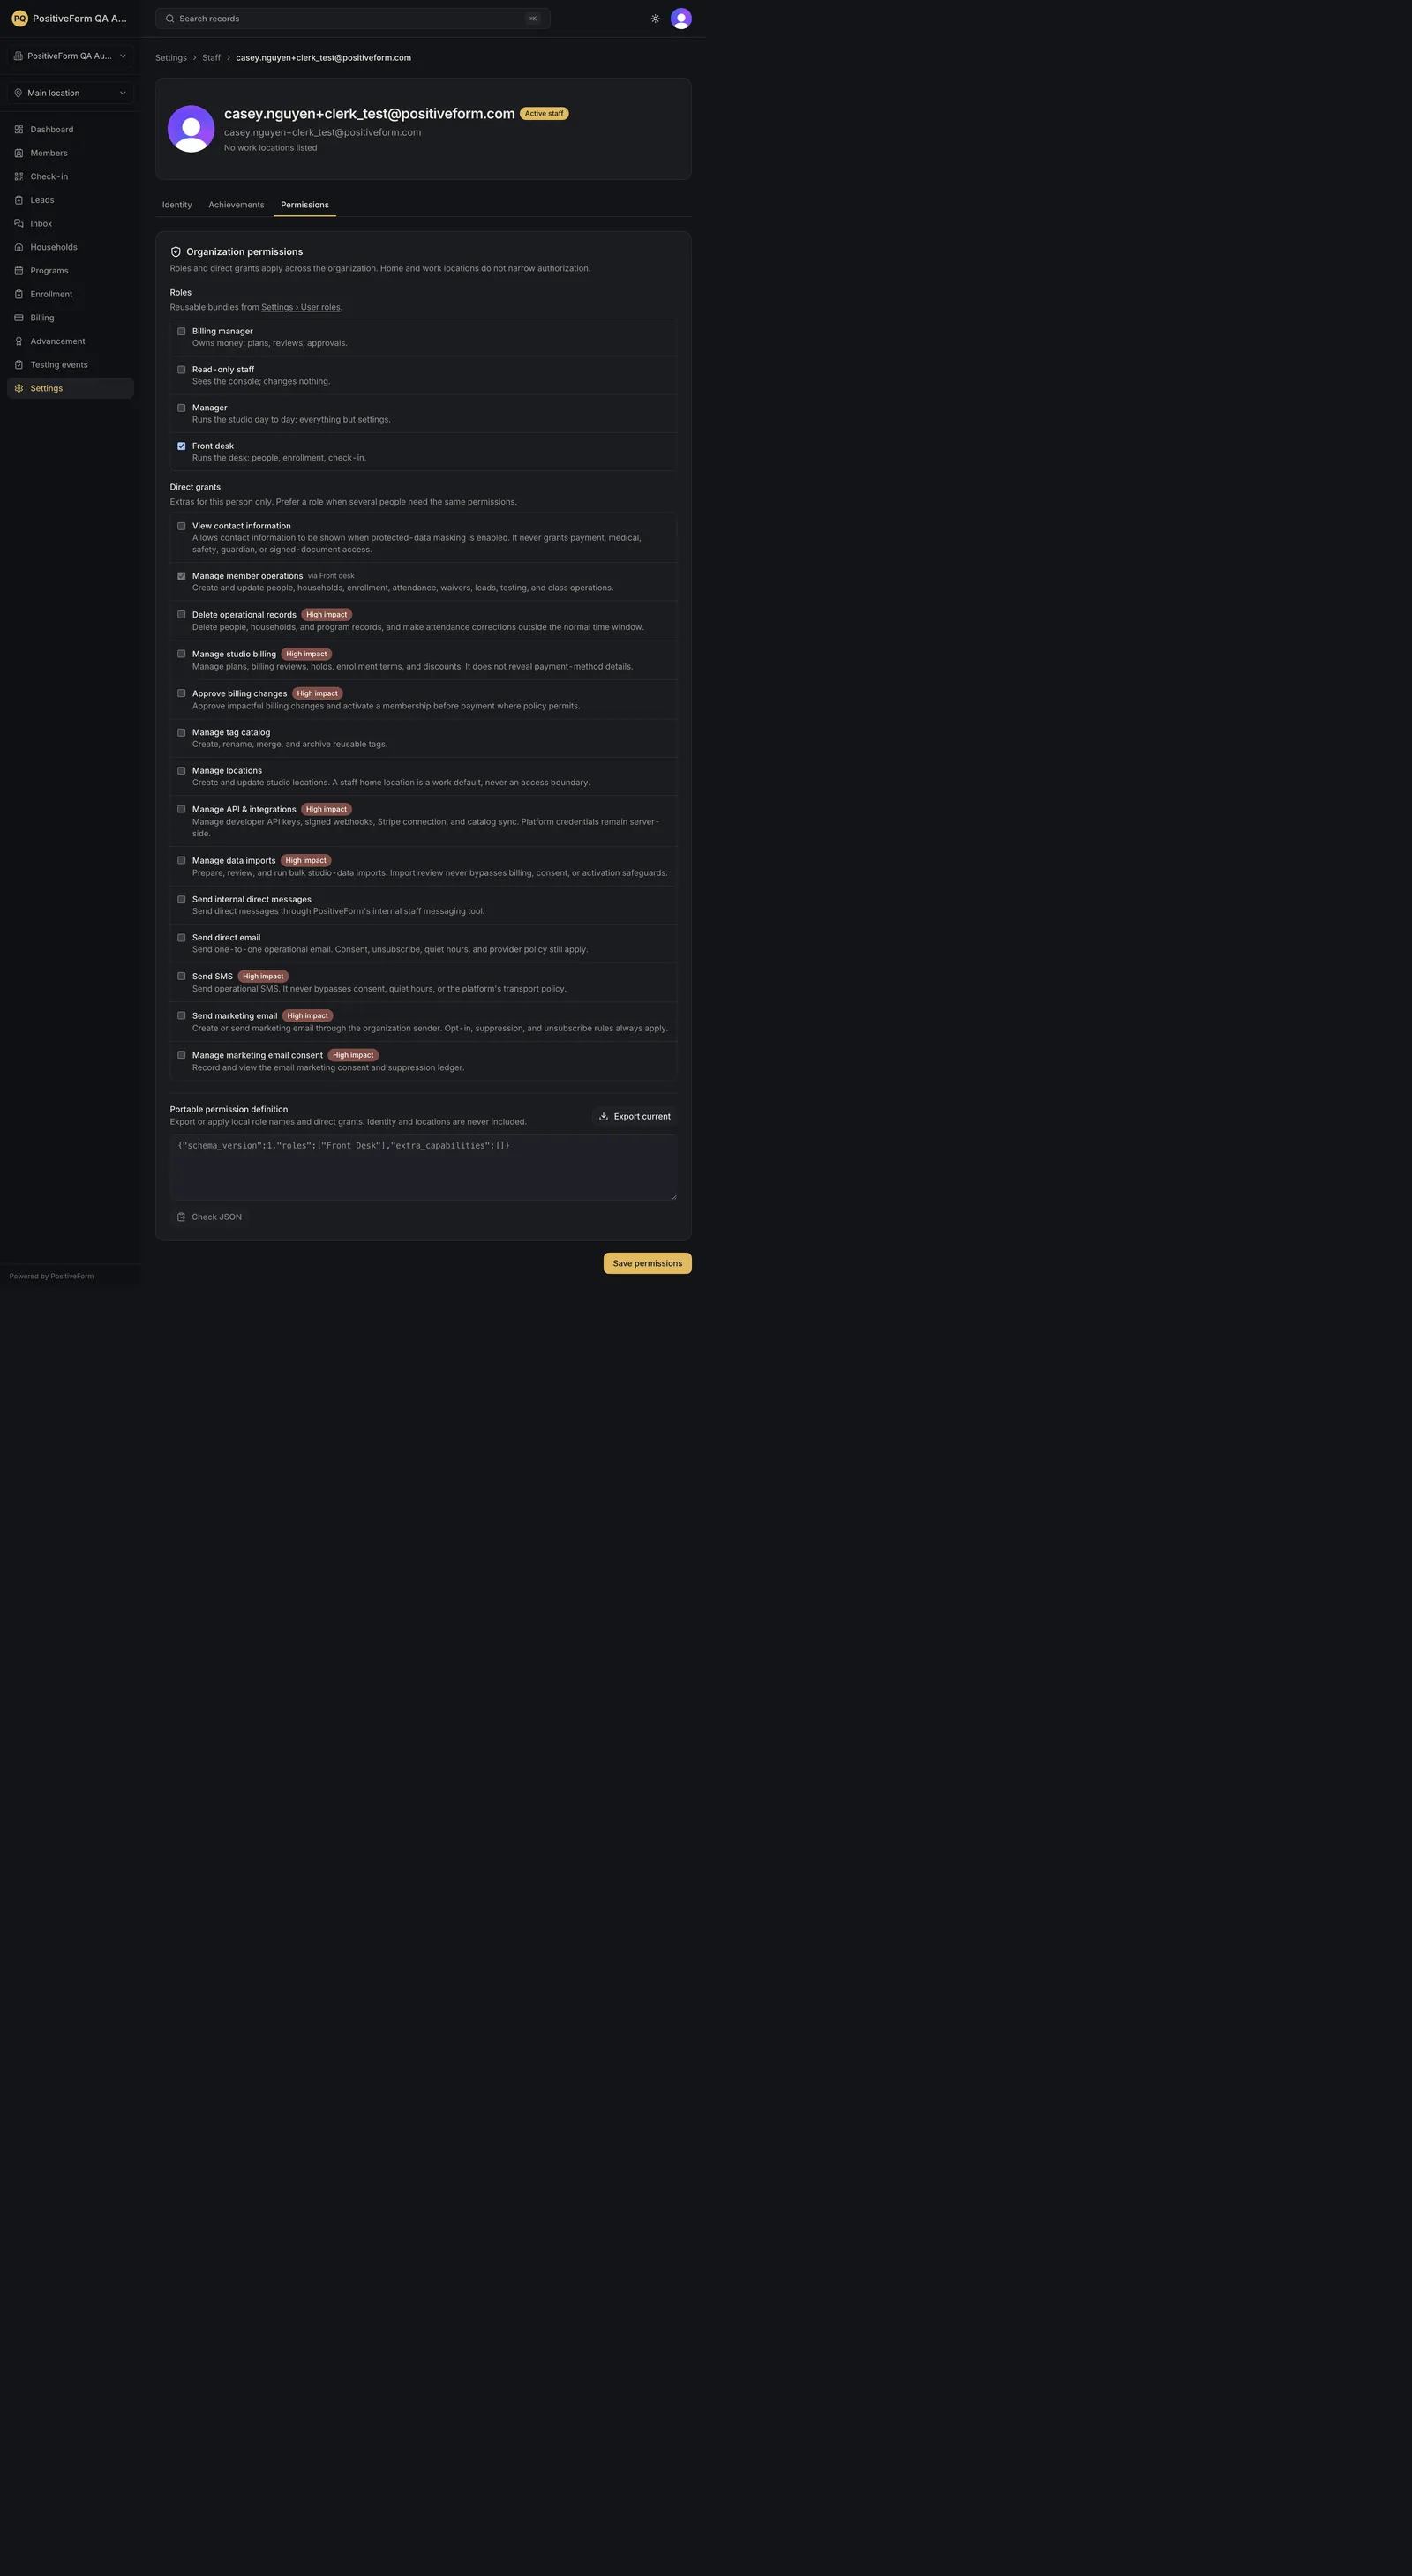
- Click the Permissions tab. It opens on Organization permissions, which restates that roles and direct grants apply across the organization and that locations do not narrow authorization.
- Open the Roles selector and choose every role this person should hold. They get the combined permissions of all of them. The card links to Settings › User roles, and if none exist yet the selector says No roles exist yet.
- Under Direct grants, tick anything this one person needs that no role covers. Each label says what it lets someone do, and the riskiest carry a High impact badge.
- A permission already arriving through a role is ticked and greyed, labelled via the role or roles granting it. You cannot grant the same thing twice, and you cannot remove it here; change the role instead.
- Click Save permissions.
Move a set of permissions between people or studios
- Use Portable permission definition to move access without moving a person. Export current puts this person's local role names and direct grants in the box as JSON. To apply a definition you have, paste it in, click Check JSON, read the summary of how many roles and direct grants it carries, then click Apply JSON. Apply JSON appears only after the definition validates. Identity and locations are never included, so a definition carries access and nothing personal.
Expected outcome
PositiveForm confirms with Permissions updated, and the tab shows what this person now holds: roles ticked, direct grants ticked, and anything arriving via a role marked as such.
The result stays inspectable. You can see not just what someone can do but why, because a permission coming from a role names that role. That is what makes access reviewable later, when whoever set it up is not in the room.
Their identity, work locations, teaching status, and login access are untouched; those live on the Identity tab. If someone cannot sign in at all, check PositiveForm organization access there before changing anything here.
For an owner, the tab shows Owner permissions and nothing to edit.
Screenshots
Recovery
If saving fails, PositiveForm shows Could not update permissions. and the person's access is unchanged.
If you click Check JSON with an empty box, you get Paste valid staff-permissions JSON first. If the definition is rejected, you get That staff permissions JSON is not valid. Nothing is applied until a definition validates, so a bad paste cannot half-apply.
If a permission will not untick, it is arriving through a role, and the label names which one. Either remove that role from this person, or change the role in Manage reusable roles if nobody should have it.
If someone has more access than you intended, look at their roles first. A single role can carry a lot, and a direct grant is often not the cause.
If the tab shows Owner permissions, this person is an owner, and ownership is not changed from here.
Related guides
- Manage reusable roles — create and edit the reusable roles you assign here.
- Preview a role safely — see what a role reaches before you give it to someone.